Cyber Security and Technology Architecture: What UK SMEs Need to Review
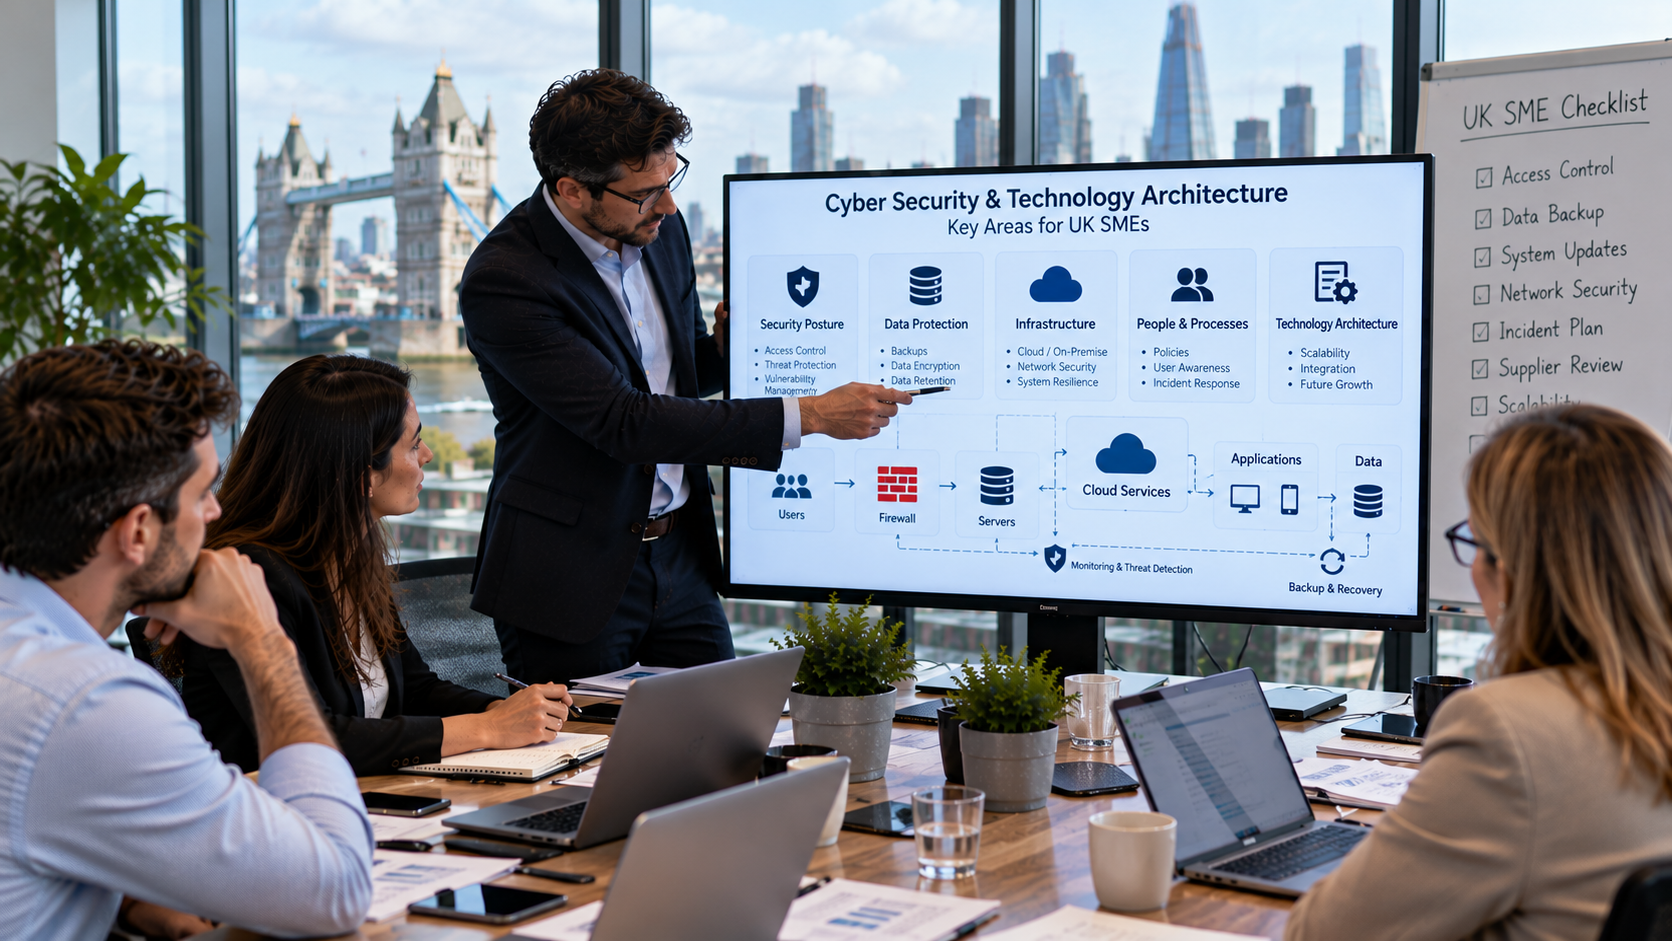
Cyber security should be built into
technology architecture, not added later. Explore practical areas UK SMEs
should review across systems, access, data and monitoring.
Cyber
security is often discussed as a separate technical function, but
for a modern business it is closely connected to architecture and operations. A
new application changes how data moves. A new employee changes access requirements.
A new integration creates another connection. Security therefore needs to be
considered whenever the technology environment changes.
One of the first tasks is understanding the
environment. Businesses should know which applications they rely on, where
important data is stored, who can access it and which external suppliers are
involved. The NCSC’s small organisation guidance emphasises
practical measures such as securing email, protecting devices, backing up data
and securing important online accounts.
Identity and access management deserves
particular attention. Employees, contractors and service accounts should have
appropriate access rather than broad permissions by default. When people change
roles or leave the organisation, access should be reviewed. Strong
authentication and clear ownership can reduce the impact of compromised
credentials.
Data protection is another major
consideration. Businesses should identify sensitive information and determine
how it is protected in transit, at rest and during storage or disposal. The
NCSC recommends a risk-based approach to data security,
while the ICO provides guidance on the UK GDPR principles and data protection
by design.
Architecture also affects resilience.
Systems that depend on one undocumented integration or one employee may work
until something breaks. A technology audit can identify these single
points of failure and help the business decide whether to add redundancy,
improve documentation, replace outdated software or introduce monitoring.
Security monitoring should be proportionate
to the business and its risks. Logging can help establish what happened during
an incident, while monitoring can provide earlier visibility of unusual
activity. The objective is not to collect every possible log without purpose,
but to create enough visibility to detect and investigate meaningful events.
For businesses building or replacing
software, secure architecture should be part of the
design process. Nexteck’s UK-led architecture offering describes practices such
as architectural blueprinting, DevSecOps setup, environment separation and
security testing. The exact controls needed will depend on the application and
regulatory context, but the principle is consistent: security is easier to
maintain when it is designed into the system. For further context, see ICO UK GDPR
guidance.
A
strong security programme is therefore not a single product purchase. It is an
ongoing combination of architecture, people, access controls, data
protection, monitoring and response. UK SMEs can make meaningful progress by
first understanding their environment, prioritising the highest risks and
building security improvements into the wider technology roadmap. For further
context, see ICO
data protection by design.